Changelog
Follow up on the latest improvements and updates.
RSS
new
Enterprise
Signature
Access & Security
Workspace: Service Accounts

Integrations no longer have to run on a person's login. Service accounts are workspace-owned identities with their own scoped, rotatable credentials, created and managed by Administrators in Workspace Administration.
Key Highlights
- Workspace-Owned Identity: A service account belongs to the workspace rather than an employee, so an integration keeps running through role changes and departures, and it does not consume a paid seat or allow interface sign-in.
- Least-Privilege Access: Grant each account only the solutions, tables and scopes it needs, chosen one at a time, instead of inheriting whatever its creator happens to have.
- Named, Revocable Credentials: Generate a key with a name you will recognize in logs, copy the full value the one time it is shown, and revoke it on its own without disturbing the account's other keys.
- Rotation Built In: Set a client secret expiration and a rotation policy, see the resolved expiry date on the account, and rotate with overlap so integrations keep working at cutover.
- Access Reviews: Every account carries a named owner, a backup owner, its authentication method, its granted scopes and its last-used date, so a quarterly review can cover non-human identities with the same evidence you collect for people.
- Contained Blast Radius: Rate limits, usage alerts and allowed IP ranges bound what a credential can do even if it is exposed.
How It Works
- Open Service Accounts under Workspace Administration to see every account with its authentication method, status and last use, filterable and searchable by name.
- Create an account through a guided flow with four steps: Details, Authentication, Security and Access.
- In Details, name the account, describe what it is for, and assign a named owner and a backup owner who takes over if the owner is deactivated.
- In Authentication, choose OAuth 2.0 for production system-to-system integrations or an API token for simple scripts, then set the client secret expiration and rotation policy.
- In Security, set rate limits, usage alerts and any allowed IP ranges that the account's credentials are restricted to.
- In Access, add the solutions and tables the account may reach and pick a scope for each one, such as reading or writing records.
- Generate a key when you are ready, copy it straight into your secrets manager, and revoke or rotate it later from the account's Keys section.
- Disable an account from its status toggle to cut off access immediately without losing its configuration.
Non-human identities are now governed the way people are: owned, scoped, time-bound and reviewable.
new
All Plans
AI Platform: Support for Azure API Gateway

Organizations that expose their models only through a corporate API gateway can now connect SmartSuite AI to them. Azure connections accept custom request headers and a custom deployment path, so requests arrive at your gateway in the exact shape it expects.
Key Highlights
- Gateway-Ready Connections: An Azure connection can now sit behind a corporate API gateway rather than calling the model endpoint directly, which is the only route available in many enterprises.
- Custom Request Headers: Add the header name and value pairs your gateway requires, such as its subscription key, and they are sent with every AI request SmartSuite makes on that connection.
- Custom Deployment Path: Point the connection at a non-standard base path when your gateway does not mirror the provider's default URL structure.
- AI Governance: Route AI traffic through the gateway your security team already monitors, so prompts and responses stay inside the logging, policy and rate-limiting controls that govern every other AI call your organization makes.
- Cost Allocation and Approval Routing: Carry chargeback codes or approval group headers on the connection, so AI usage is attributed to the right cost center and routed to the right reviewers without any extra work in SmartSuite.
- Secrets Handled as Secrets: Header values are stored encrypted with the connection and masked after saving, alongside the credentials already held there.
How It Works
- Open the AI Control Center and create or edit an Azure connection.
- Enter the endpoint, API version and key as you do today.
- Add each custom header your gateway expects as a name and value pair.
- Set the deployment path if your gateway fronts models on a non-standard base path.
- Save the connection and scope it to the solutions and AI features that may use it.
- Use it from the AI Field Agent or the AI Workflow Agent automation action; every call carries your headers.
AI governance no longer has to mean turning SmartSuite AI off. The gateway stays in the path, and your teams get the features.
new
Enterprise
Signature
SmartSuite Script Engine
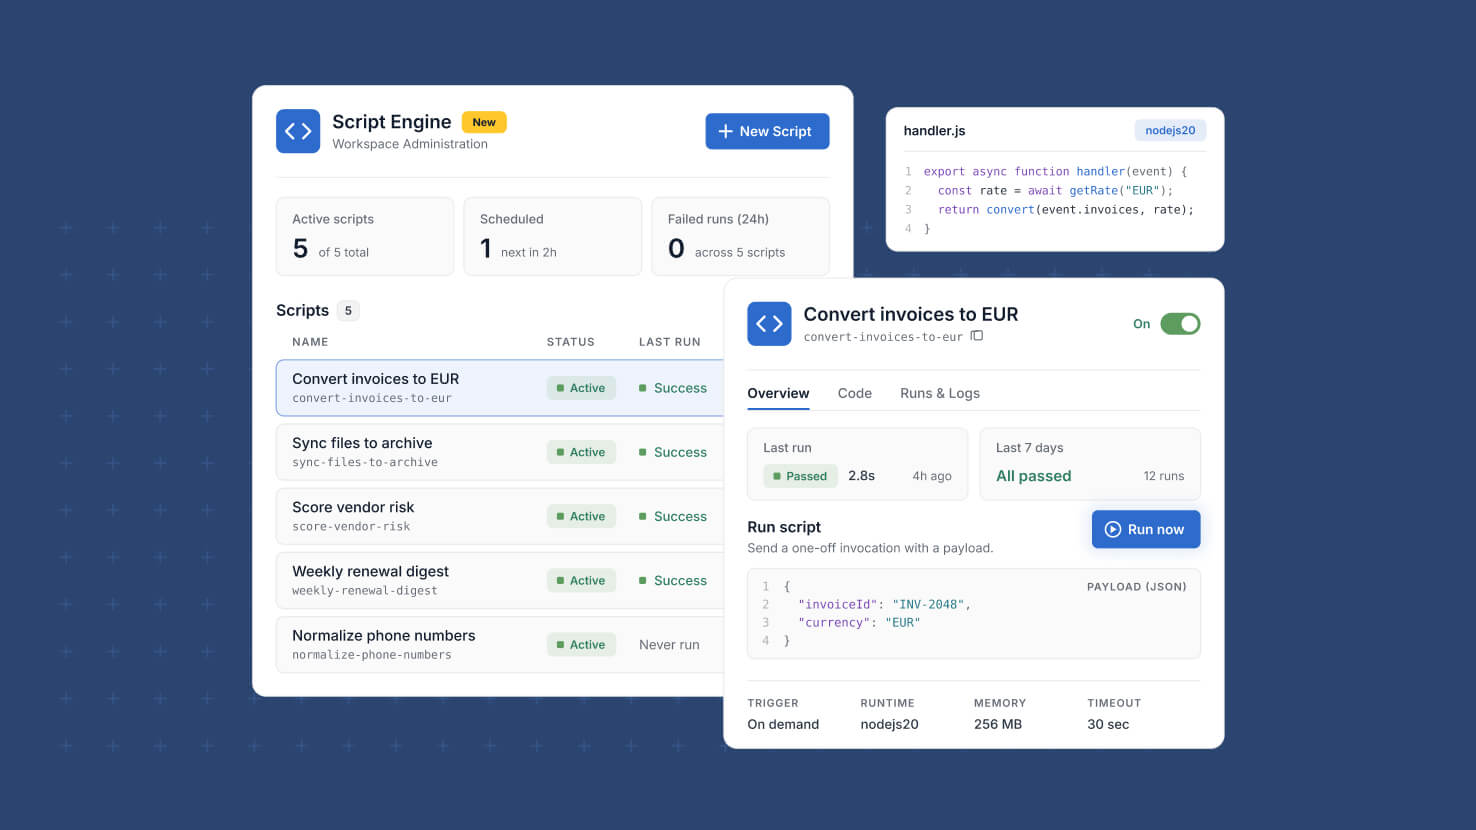
Scripts that sync data or call external services have needed a home where administrators can see what exists, when it runs, and whether it worked. Script Engine is that home: a new page in Workspace Administration to create, schedule, and monitor the JavaScript scripts in your workspace.
Key Highlights
- One Script Directory: Every script in the workspace in one list, showing status, schedule, and recent activity, with columns you can show, hide, or reset.
- Health At A Glance: Counts for active scripts, scheduled scripts, and failed runs in the last 24 hours sit above the list, and each one filters it in a click.
- Built-In Code Editor: Write or paste JavaScript, then set Memory and Timeout limits for each script.
- Secrets By Reference: Choose which workspace secrets a script can use, so credentials never live in code and rotate in one place on the Secrets page.
- Flexible Scheduling: Run scripts Hourly, Daily, or Weekly, or on a custom rate or cron expression.
- Run History: Every run is recorded with its execution mode and the script version that ran, with filtering, sorting, and per-run details.
- Evidence Collection On A Schedule: A daily script can pull control evidence from an external system into your compliance records, and its run history shows each collection ran.
How It Works
- Open Workspace Administration and select Script Engine, directly above Secrets.
- Create a script and enter a name and a Script ID of 3 to 63 lowercase letters, numbers, and hyphens, unique within the workspace.
- Write the JavaScript, set Memory and Timeout, open Choose secrets to tag the secrets it needs, and save.
- Saved scripts are validated, and the status badge shows Active, Inactive, or the validation failure, with the reason on hover.
- Duplicate a script to try a change safely; the copy needs its own Script ID before it saves.
- Export the script list to CSV, Excel, or Google Sheets, or a single script to JSON with secret references and never secret values.
Script Engine gives every script in the workspace a clear record: what it does, when it runs, which secrets it uses, and how each run went.
improved
All Plans
Filter Widget: Multiple Operators in Dynamic Filters
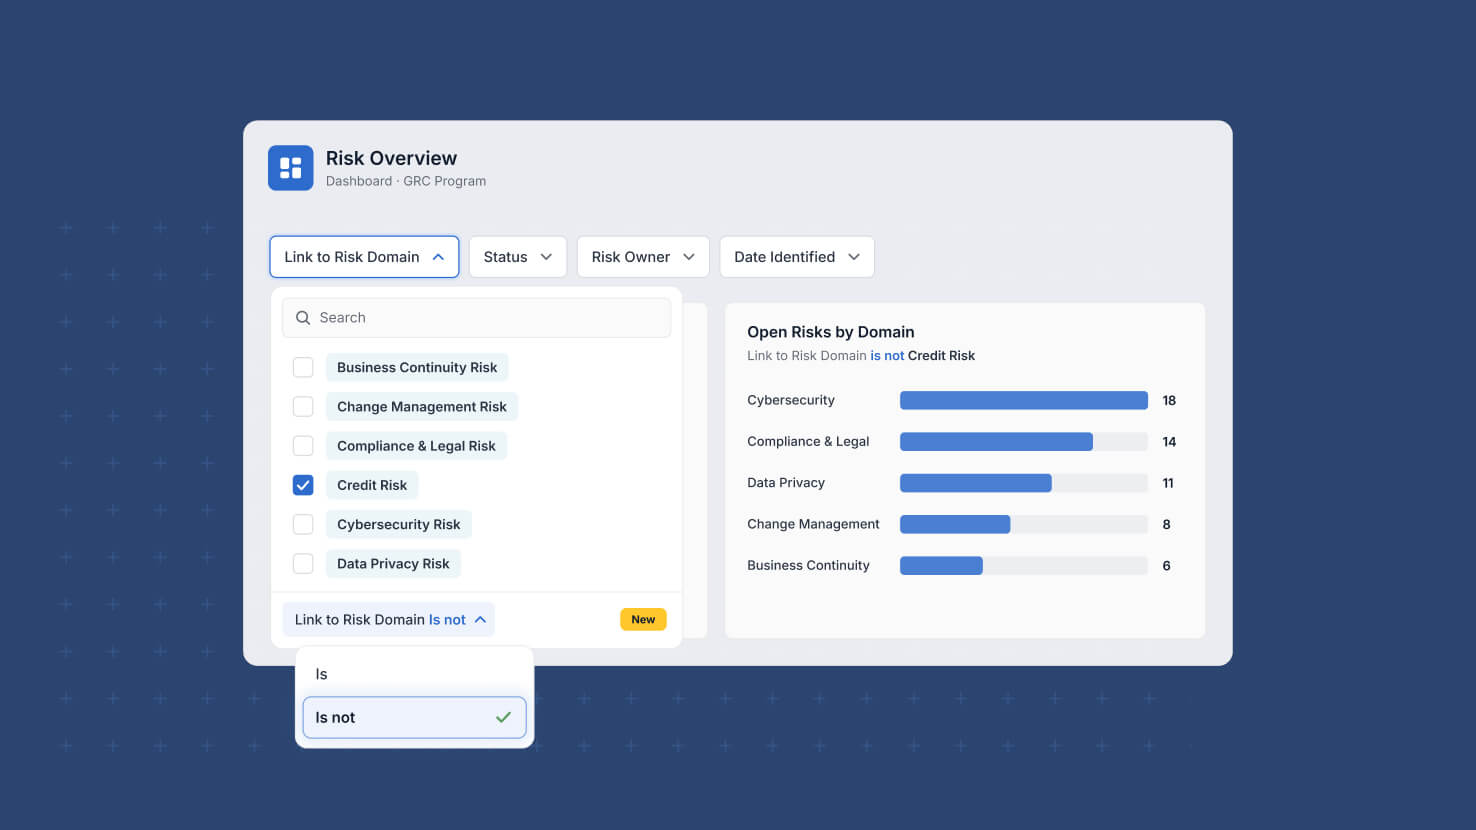
Dynamic filters on a dashboard could only ask one question: is the value this. Filtering a widget to everything except a status, or everyone other than one person, meant building a second widget to get there. Dynamic filters now carry an operator you choose, so a single control can include or exclude.
Key Highlights
- Is And Is Not: Every dynamic filter now supports both operators, so one control can narrow to a value or exclude it.
- Operator Per Filter: Each filter in the widget carries its own operator, so one can include while another excludes in the same set.
- A Chosen Default: Pick the condition that is pre-selected when someone expands the filter, instead of always starting from Is.
- Changed On The Dashboard: Viewers switch the operator from the filter's footer without opening widget settings or editing the dashboard.
- Open Work At A Glance: Exclusion makes the common service view simple, filtering a ticket dashboard to Status is not Closed without a second widget.
How It Works
- Open the widget's Filters tab, add a dynamic filter on a field, and set its Default Condition to the operator you want pre-selected.
- The Default Condition setting sits alongside Selections, Default Value and Sort Values in the filter's settings dropdown.
- On the rendered widget, the filter footer shows the field label next to the operator as a dropdown, for example Status Is.
- Viewers change the operator there, choose values, then apply by clicking Apply, clicking outside the control, or pressing Enter.
- Conditions from the filter widget combine with a connected widget's own filters using AND, so the widget's existing filters are preserved.
Dynamic filters can now exclude as easily as they include, with the default condition yours to set and the operator the viewer's to change.
improved
All Plans
Recycle Bin: Restore Team
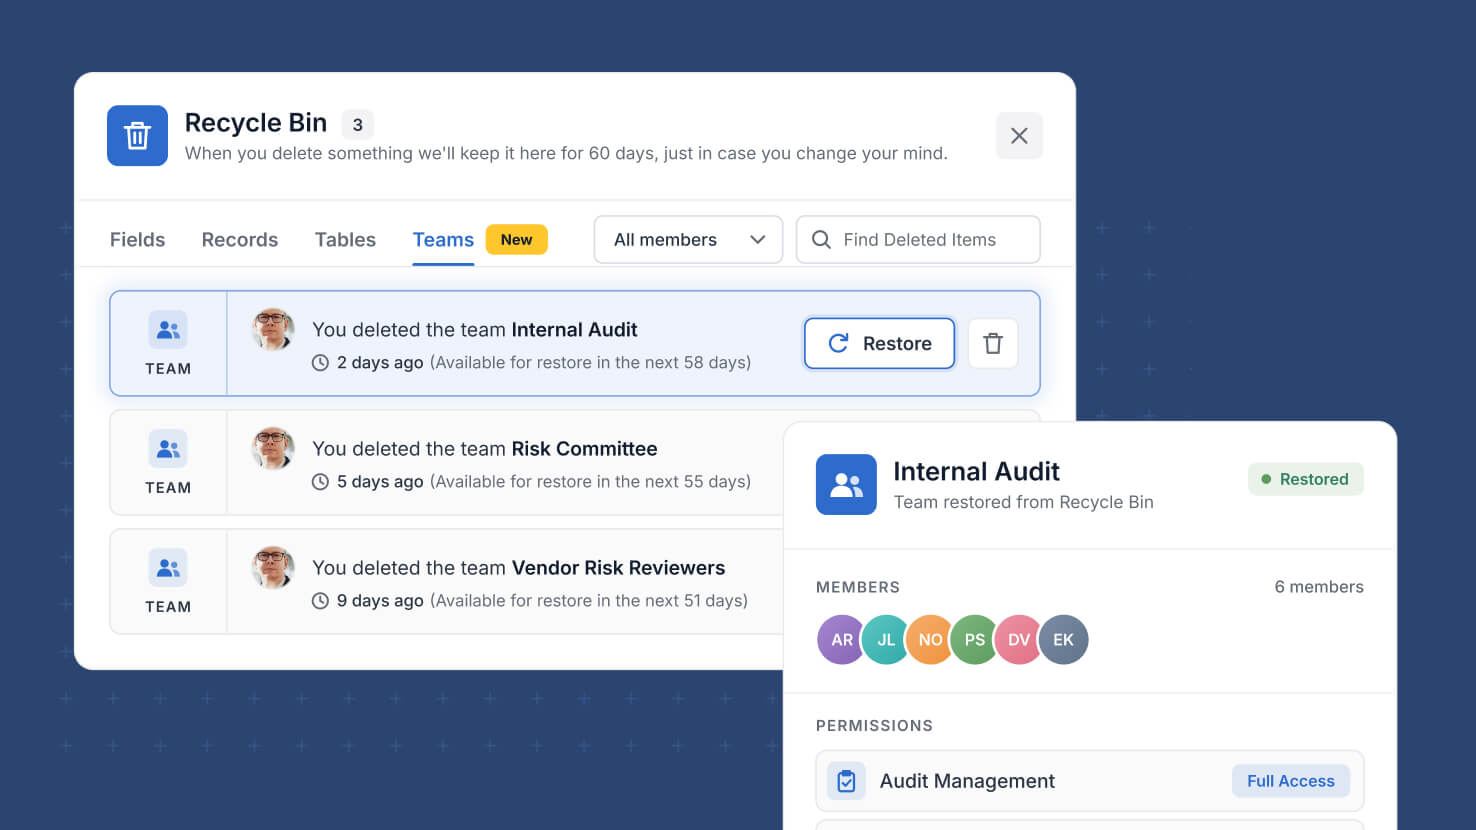
Deleting a team used to be final, which made the safe move leaving unused teams inactive rather than removing them. Deleted teams now go to the Recycle Bin, where an Administrator can restore one.
Key Highlights
- Teams Are Recoverable: A deleted team now moves to the Recycle Bin instead of disappearing, so an accidental delete is no longer permanent.
- Administrator Restore: Members with the Administrator role restore a deleted team from the Recycle Bin, alongside the other items collected there.
- Membership Comes Back: Restoring a team returns it with its members, so you are not rebuilding the roster by hand.
- Cleaner Team Lists: With deletion reversible, you can remove teams you no longer use instead of parking them as inactive to stay safe.
- Access Reviews: Teams grant permissions, so recovering one that was removed in error keeps an access review from turning into a rebuild.
How It Works
- Delete a team as before, from Workspace Administration, Manage Teams, by opening the team and choosing Delete Team.
- The team moves to the Recycle Bin rather than being removed outright.
- Open the Recycle Bin, find the team among the deleted items, and choose to restore it.
- The restored team reappears in Manage Teams and can be used again wherever teams grant access.
- Setting a team to inactive is still there when you want to keep it in place but stop it granting permissions.
Removing a team is now a reversible action, so tidying up your workspace no longer carries the risk it used to.
new
Enterprise
Signature
Managed Secrets
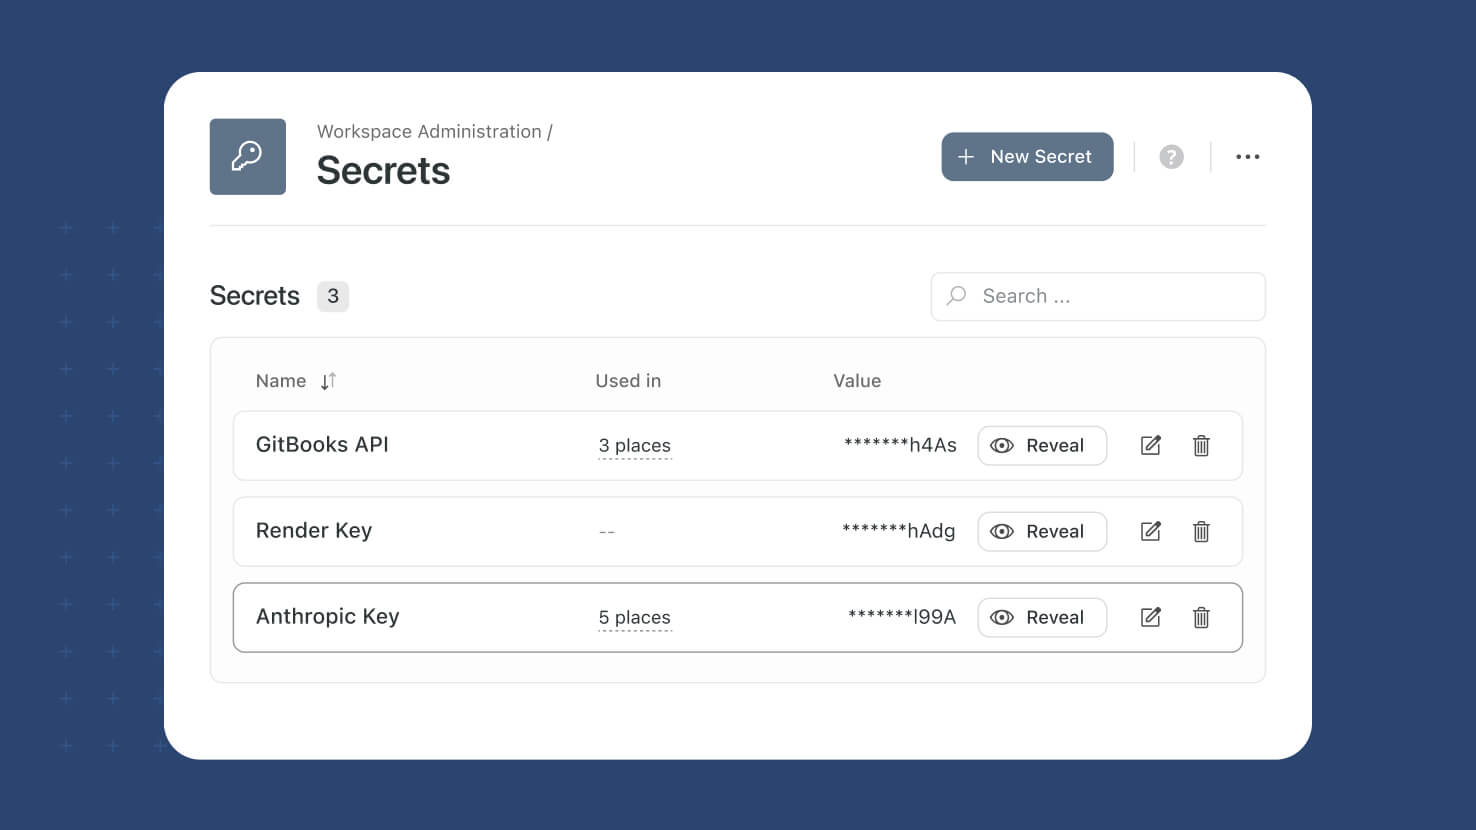
API keys and tokens sitting inside script code are a liability every auditor asks about. Secrets now has a page of its own under Workspace Administration, where you store sensitive values once, reference them by name, and see exactly who revealed each one and when.
Key Highlights
- Dedicated Page: Secrets has moved out of the Script Engine and onto its own page in the left sidebar, directly below Script Engine.
- Values Out Of Code: Scripts and integrations reference a secret by name, so API keys, tokens and connection strings never appear in the script itself.
- Reveal Is Recorded: Every reveal saves the member's name and the time, giving Administrators an access trail for sensitive credentials.
- Usage Before Changes: The Used in column shows every script and integration depending on a secret, so you can check impact before rotating or deleting it.
- One Rotation, Everywhere: Updating a secret's value takes effect in everything that references it, so rotating a credential is a single edit.
How It Works
- Open Workspace Administration and select Secrets to see the list, search it by name, and sort by secret name.
- Create a secret with a name and a value. The value is encrypted on save, and only its last four characters are ever shown in the list.
- Revealing a value takes two steps: a warning that the action is recorded, then the full value in a read-only field with a Copy button.
- Editing lets you rename a secret without breaking references, or type a new value to overwrite the existing one. Values are write-only and never displayed.
- Deleting a secret that is in use lists the affected scripts and integrations, turns them off, then removes the secret. The action cannot be undone.
Credentials now live in one governed place, with a record of every reveal and a clear view of what depends on them. Available now under Workspace Administration.
new
All Plans
Mobile
Mobile: Data Schema Widget
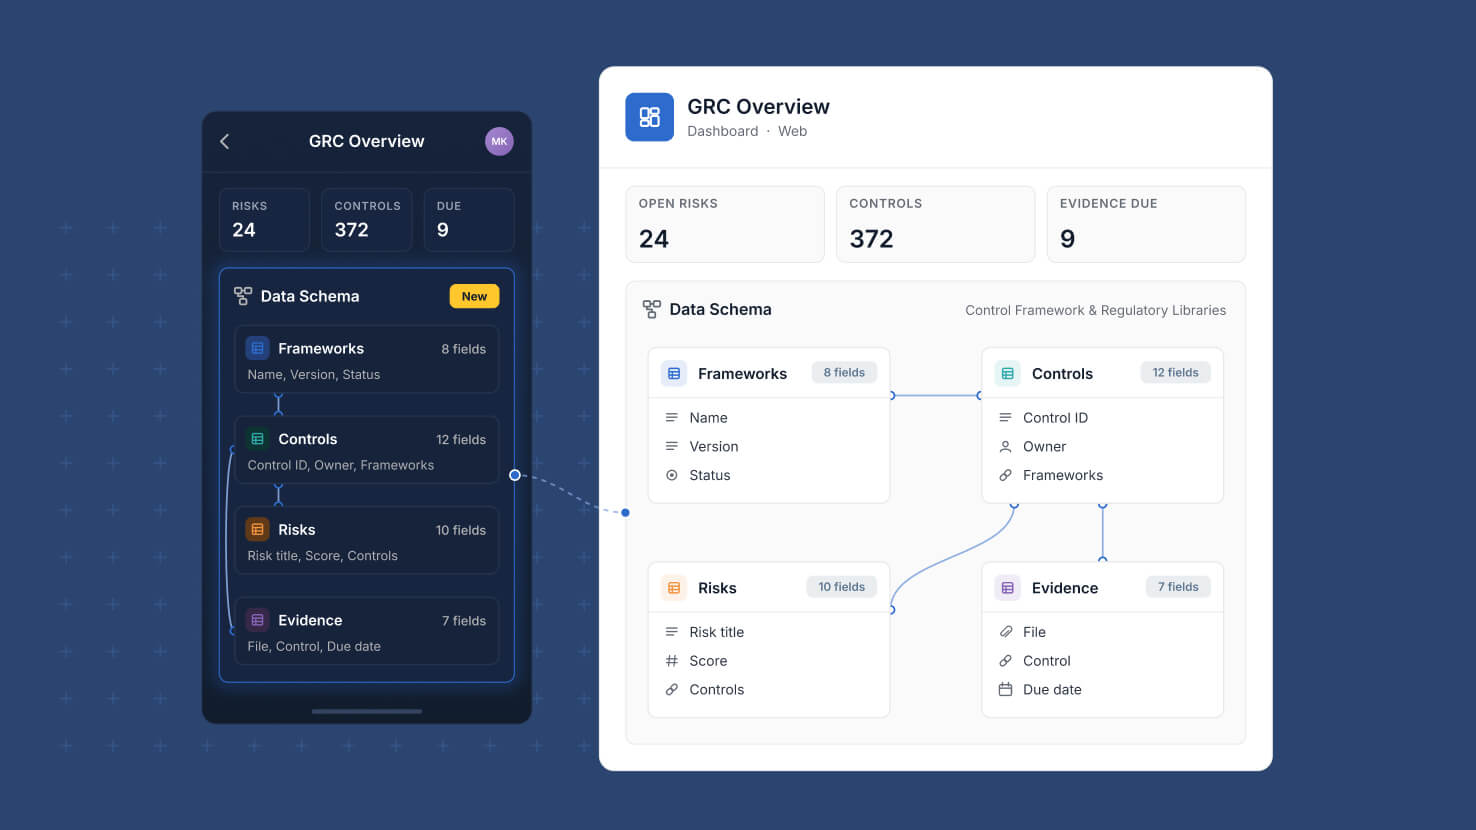
The map of how your tables connect is no longer something you have to be at a desk to read. Data Schema widgets now render on mobile dashboards, with the same table cards, relationship lines and automatic layout the web shows.
Key Highlights
- Schema On Mobile: Data Schema widgets now draw on dashboards in the mobile app instead of leaving an empty space on the card.
- Same Diagram As Web: Table cards, field lists, relationship lines, self-links and automatic layout match what the same widget shows on the web.
- Pan And Zoom: Unlock the card to pan and pinch to zoom the diagram without the dashboard scrolling underneath you.
- Full Screen View: The expand icon opens the diagram full screen, with zoom in, zoom out, fit to screen, and double-tap to reset.
- Permissions Respected: Tables a member cannot access, and the relationship lines running to them, are left out of the diagram.
How It Works
- Open a dashboard in the mobile app and the diagram scales to fit its card, with the widget name and description shown above it.
- Tap the padlock to switch the card between scrolling the dashboard and moving the diagram, then tap it again to resume scrolling.
- Relationship lines are drawn from Linked Record, Count, Rollup and Lookup fields. Member and team fields do not create lines.
- Configuration stays on the web, so settings such as showing all fields or including cross-Solution links carry over the next time the dashboard loads.
- If the widget has no Solution selected, or its Solution was deleted, a clear message appears in place of a blank card.
Anyone with access to the dashboard can now read a Solution's structure from a phone or tablet. Available on all plans.
new
All Plans
Mobile
Mobile: Pivot Table Widgets on Dashboards
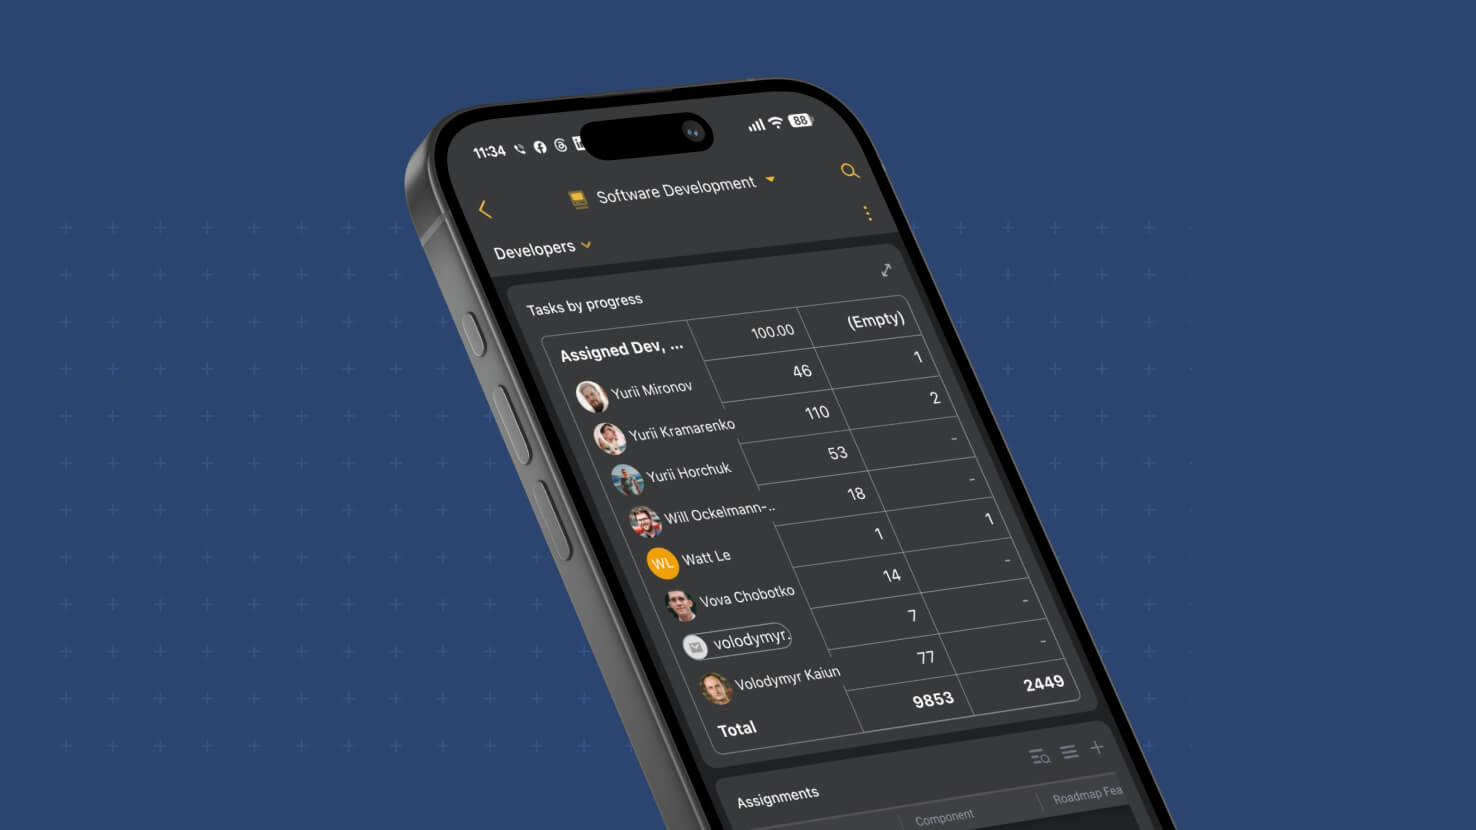
Pivot Table widgets now come along when your dashboards go mobile. A dashboard that contained a pivot used to show an empty space in its place in the SmartSuite mobile app, which left out one of the most useful summary views for anyone checking numbers away from a desk. The widget now renders on phone and tablet with the same cross-tab you see on the web, and it stays interactive: tap through to the records behind any number, or open the table full screen for a closer look.
Key Highlights
- The Same Numbers As The Web: Rows, columns, cell values, row and column totals and the grand total all match the web app, in light and dark themes.
- Formatting That Follows The Field: Currency, percent, precision, prefixes and suffixes display the way the summarized field is configured, and a combination with no records shows a dash.
- Pinned Headers: The header row and the first column stay in place while the rest of the table scrolls in both directions.
- Tap Through To Records: Tapping a cell opens exactly the records counted there. Row and column totals open that row or column, and the grand total opens every record behind the widget.
- Full Screen Tables: An expand icon in the widget header opens the pivot on its own screen, sized to the device, with drill-in still available.
- Record Selector Aware: A pivot scoped by a Record Selector widget follows the selected record, and its drill-in stays scoped to it.
- Built For Large Tables: Column widths authored on the web carry over, and tables at the 1,000-row or 1,000-column maximum load quickly and scroll smoothly.
How It Works
- Build or edit the Pivot Table widget on the web as usual. Configuration stays on the web, and the mobile app displays the result.
- Open the dashboard in the mobile app and the pivot appears in place, with its title and description.
- Scroll horizontally and vertically through the table, then tap any value or total to see the underlying records. Going back returns you to the dashboard.
- Tap the expand icon to view the table full screen.
- If a widget's row or column field has been removed, or you cannot access its table, the widget shows a clear message instead of an empty space.
The summaries your team relies on now travel with them. Available on all plans.
improved
All Plans
AI: Updated Supported Models
The model picker in the AI Control Center has been brought up to date. The current generation from each provider is now available when you create an AI connection, models their providers have retired are no longer offered, and the price and capability details shown next to each one have been corrected.
Key Highlights
- Current Generation Models: The latest Anthropic, OpenAI, Google Gemini and xAI models are now selectable when you create or edit an AI connection.
- Retired Models Removed: Models their providers have shut down no longer appear for new connections, so you cannot pick one that fails on its first call.
- Accurate Tiers: Cost tiers and capability descriptions now match each provider's current pricing and documented inputs, including PDF and image support.
- Existing Connections Untouched: Connections already set up keep the model they are on, so running AI fields and automations are not affected.
- Budget Options At Every Level: Low-cost models sit alongside flagship ones, so high-volume tagging, extraction and summarization do not have to run on a premium model.
How It Works
- Open the AI Control Center and create or edit an AI connection to see the refreshed picker.
- Each model shows its provider, cost tier and the input types it accepts, so you can match the model to the job before you save.
- To move an existing connection onto a current model, edit the connection and choose the new one. The change applies to everything using that connection.
- Workspace Administrators manage AI connections, so the models in play stay consistent for everyone building in the workspace.
Choosing a model is now a decision about cost and capability rather than a guess about whether it still runs. The refreshed catalog is available now in every workspace where AI is enabled.
new
All Plans
Automations & Integrations
SmartSuite MCP Server
Your workspace is now reachable from any MCP-compatible AI assistant. The SmartSuite MCP Server is a hosted connector that lets an assistant explore your Solutions, work with records, and build and inspect configuration, acting as you and bounded by your own permissions. There is nothing to install and no API key to manage.
Key Highlights
- Zero Install: Connect from any MCP-compatible client at a hosted URL, with no API keys and nothing to run locally.
- Acts As You: Every call runs under your own sign-in, so an assistant sees and changes exactly what you could, never more.
- Scoped Consent: At connection you choose read-only or read and write, and which Workspaces the grant covers. Read-only is the default.
- Full Workspace Reach: Explore Solutions and Tables, search and edit records, manage comments and files, build Tables, Fields and Forms, and inspect Automations.
- Audit Trail Built In: Changes appear in the existing activity history attributed to both you and the assistant that acted for you, which matters for change management and evidence capture.
- Admin Control: Workspace Administrators set MCP access per user as Disabled, Read-Only, or Read and Write.
How It Works
- In Claude, open Customize, then Connectors, search for SmartSuite and click to connect.
- You sign in through SmartSuite's standard login, including social sign-in and SSO with multi-factor authentication where your organization requires it.
- On the consent screen you pick the Workspaces to share and whether the assistant may write. Read only and specific Workspaces are selected by default.
- Behind the scenes the connector uses OAuth with PKCE, so no password or API key is ever handed to the assistant.
- Workspace Administrators govern who can connect at all, and a user's existing Role and Permissions still bound everything the assistant can reach.
- Reads come back bounded by default, returning record title and URL rather than every field, so sessions stay fast and inexpensive.
Any assistant your team already uses can now work inside SmartSuite under your identity and your permissions. Available to all customers.
Load More
→